🛑 Is ModHeader safe to use in 2026?
No. In July 2026 Google flagged ModHeader as malware and Microsoft removed it from the Edge store, after researchers found build 7.0.18 collected the domains you visit via a hidden SDK. Remove it and switch to a maintained alternative.
📂 Can I export and version control configs?
Each link carries one Profile name, its enabled valid request headers, and valid Request Filters. Treat the complete link as sensitive if it contains credentials.
🔒 Does the share page send my data anywhere?
The payload stays after # in the URL, which browsers do not include in the request for the /s page. The preview masks common sensitive keys, but the complete link still contains the configuration.
🌐 Will my rules apply to all sites?
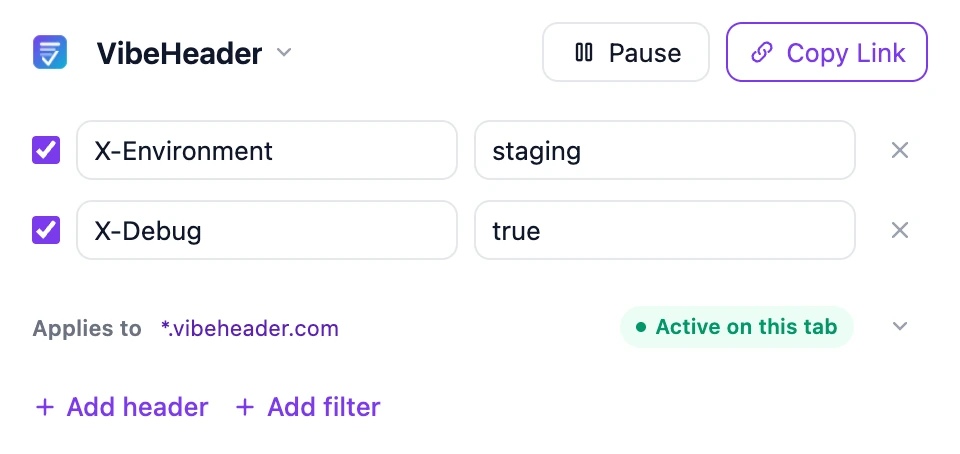
Only requests matching an enabled Profile’s Request Filters receive its headers. With no enabled filters, that Profile applies to all supported requests. Test the exact target URL before relying on a rule.
🔧 What if I need redirects or mocks?
For complex needs, try Requestly or desktop proxies. For headers only, VibeHeader is simpler.
🛡️ Security tips?
Share only with trusted teammates, avoid long-lived secrets, rotate values periodically.